SeniorCRE
§ AI Governance Posture
The governance question isn't which model. It's who signs.
Intelligence does not confer authority.
As AI moves from answering questions toward influencing operations, the decisive question is no longer what the model can do. It is what information the model is authorized to treat as true, what it may infer, what it may recommend, and who remains accountable for the decision.
Coherence Before Intelligence. The Operator-Controlled Operating Record and integrated authority policies are designed; operator validation remains pending.
Explore the two authority policies · Review the Trust Center evidence
Coherence Before Intelligence
The operator governs what is true—and what may be done.
Truth policy
Which information governs this purpose?
- Approved definitions and effective periods
- Operator-designated source authority
- Reconciliation and exception rules
- Evidence and source lineage
- Named human adjudication
Action policy
What may be done, by whom and under which conditions?
- Permissions and decision rights
- Use classes scaled to consequence
- Separate human approvals
- Execution and tool boundaries
- Audit, refusal and escalation
An agent can be authorized to act without being authorized to choose which conflicting number governs.
Permission to act does not equal authority to determine truth. This integrated policy model is designed, not verified operator enforcement. Model confidence never creates organizational authority.
Capability & evidence status
What exists today, as of October 22, 2026
Component status describes controlled-environment progress only. The Operator-Controlled Operating Record as a whole is designed and not yet implemented in any community as of October 22, 2026; no operator-production deployment or measured operator outcome is claimed.
What each status means
- Designed
- Specified and sequenced by readiness and acceptance gates. Not yet implemented in any community as of October 22, 2026.
- Built
- Implemented in the platform and demonstrable in a controlled SeniorCRE environment. Not validated with an operator, and not implemented in any community as of October 22, 2026.
- Built (validation-exercised)
- Built and exercised against representative (synthetic or de-identified) data in a validation environment. Not running in any operator’s production environment, and not implemented in any community as of October 22, 2026.
- Operator deployment
- A workflow accepted end to end by a named operator owner against operator data. None claimed as of October 22, 2026.
- Production evidence
- An outcome measured in operator production with source, window, method and lineage stated. None published as of October 22, 2026.
The risk belongs to the decision—not just the model.
Illustrative scenarios and proposed controls. The evidence listed is required for review, not evidence claimed to exist. No risk elimination or customer outcome is promised.
Financial
- Scenario
- A forecast uses operational occupancy where the finance policy calls for revenue occupancy.
- Proposed control
- Declare the purpose, financial definition and governing source before a recommendation.
- Accountable owner
- CFO or named finance approver
- Required retained evidence
- Source schedule, effective period, definition version, reconciliation and approved forecast assumption.
Operational
- Scenario
- Community workforce metrics use different periods or denominators in a coverage comparison.
- Proposed control
- Align the measurement scope; escalate unresolved differences before staffing review.
- Accountable owner
- COO or named operations leader
- Required retained evidence
- Metric dictionary, source cutoffs, staffing inputs, exceptions and reviewer disposition.
Clinical
- Scenario
- An AI signal influences care without an accountable licensed review.
- Proposed control
- Keep signals advisory, with licensed review and no autonomous orders or medication changes.
- Accountable owner
- Licensed clinician and clinical leadership
- Required retained evidence
- Underlying observations, scope, review, rationale and clinical escalation record.
Institutional reporting
- Scenario
- A board or lender figure cannot be reconstructed from its source and approval history.
- Proposed control
- Require source lineage, policy versions and accountable approval before release.
- Accountable owner
- Named reporting steward and signatory
- Required retained evidence
- Original evidence, authority policy, determination, approval and issued report version.
Authority stays with accountable people.
- Operator
- Declares purpose, definitions, source authority, decision rights and the named approver. Unresolved disagreements return to operator authority.
- Owner / capital partner
- Specifies reporting obligations and evidence requirements within agreed rights. Ownership does not silently transfer the operator’s authority over its operations.
- Technology provider
- Implements and tests the agreed boundaries, preserves required evidence and states limitations. Software and model confidence do not create organizational authority.
- Human reviewer
- Finance, operations and reporting signatories retain their decisions; licensed clinicians retain clinical judgment, approval and escalation.
A signal is not a clinical decision.
The proposed governance model requires licensed review for clinical-adjacent signals. It grants no autonomous diagnosis, orders, medication changes, care-plan changes or regulatory submission. This simulation contains no resident-identifiable data and no live PHI.
Clinical record surfaces are built; medication administration and eMAR remain roadmap — not built, excluded from Road 2 starting scope and unavailable for production today. The future native clinical configuration requires function-specific build completion, clinical-safety review and clinical sign-off, end-to-end workflow validation, data readiness, operator acceptance before production entry. No community runs SeniorCRE as its clinical system of record.
How it would be deployed remains the operator’s choice: after the required gates are cleared, SeniorCRE may carry defined clinical system-of-record functions, or it may run alongside an operator’s existing eMAR, reading one direction only, so one medication record remains authoritative.
One authoritative medication record per community, always. In a parallel configuration SeniorCRE reads and never writes the MAR, because two writable medication records is a patient-safety failure mode, not an integration preference.
The policy is explicit. Enforcement requires evidence.
Specified, not built.
Exists in software on demonstration data only.
Running in an operator's environment. None today.
Verified results from operator production use. None today.
Not yet implemented in any community. Built clinical record surfaces and demonstration software do not establish integrated truth/action enforcement, community acceptance or production outcomes.
- Truth policy and Operating Record · Designed
- Required evidence: Build purpose-bound definitions, source authority, reconciliation and lineage; demonstrate retained determinations and operator acceptance.
- Integrated action policy, gateway and MCP paths · Designed
- Required evidence: Verify every permitted and denied path, missing grants, expired/revoked authority, direct bypass and separate human approval before reliance.
- Human review and audit reconstruction · Verification pending for this workflow
- Required evidence: Retain evidence, exact prompt/model and policy versions, reviewer disposition and immutable history; reconstruct an accepted and a rejected case end to end.
- Tenant isolation and PHI boundaries · Trust Center governs control evidence
- Required evidence: Review function-specific access, cross-organization denial, transmission boundaries and data-handling tests before introducing private operating data.
No operator deployment, measured ROI or clinical result is established. Compliance, certification, independent testing and recovery status are governed by the Trust Center; this page does not establish those claims.
Bring one disputed number. Identify both authorities.
Review its purpose, governing definition and source; identify the approver and permitted action; agree the retained artifacts and a bounded validation step. This is a diligence conversation, not a promised deployment or outcome.
For a bounded first governed-field discussion: Founding Operator Program. Participation and subsequent implementation remain subject to the written agreement and acceptance gates.
Technical reference and diligence
Retained doctrine, use classes and reference material describe requirements and design intent—not verified operator enforcement. Safety limits, evidence gates and current readiness above govern all examples below.
Read the framework and supporting authority doctrine
Framework at a glance · SeniorCRE
Governance for agentic AI in senior housing & care
As AI assumes more consequential care and operational functions, evidence, operator-defined authority, oversight and accountability must remain aligned.
Coherence before Intelligence.
When systems disagree, the operator governs.
SeniorCRE is designed to establish an Operator-Controlled Operating Record with source evidence, operator-defined authority and decision lineage preserved. Authority is granted by the operator; evidence supports its exercise, and demonstrated performance supports its continued use.
Six controls for governed AI
- 01
Shared definitions
Common meaning across communities, teams and systems.
- 02
Source authority
Operator-defined authority for which source governs which fact.
- 03
Reconciliation
Resolve disagreements across systems and workflows under declared rules.
- 04
Decision lineage
Preserve evidence, changes and why a decision was made.
- 05
Human authority
Human approval and operator control over consequential actions.
- 06
Repeatability
Repeat the same governed process consistently across communities.
Operator Authority Chain™
- 01
Data
- 02
Truth
- 03
Decision
- 04
Execution
Operator authority spans the whole path. Model confidence never creates organizational authority.
Agent design posture
- 01
Inform
Read-only by default
- 02
Recommend
Human review required
- 03
Decide
Operator-authorized only
- 04
Act
Operator-authorized only
Agents are designed to inform and recommend, not acquire authority of their own. Unresolved disagreement requires refusal and escalation to the named human authority.
Accountability stays with the accountable people
Responsibility remains aligned to authority and control: the operator (primary), owner, community leadership, care team and clinician, technology provider, and residents and families. A model does not become the accountable decision-maker.
Why it matters for operators and owners
Liability & accountability
A clear assignment of authority and responsibility for decisions, actions and outcomes.
Operational oversight
Explicit limits on what AI may do, under which conditions and with whose approval.
Regulatory & contractual evidence
Traceable evidence of authority, review and conditions—not a guarantee of compliance.
See the mechanism · Every AI-surfaced signal
Illustrative model
1 named reviewer, 0 autonomous actions
AI can surface. Only a named human can act.
Clinical and financial signals are decision support: no diagnosis, no orders, no medication changes, and no transfer authority without accountable human review.
Illustrative exemplar of the governed workflow, modeled — not measured from an operator deployment. No operator production integrations as of October 22, 2026.
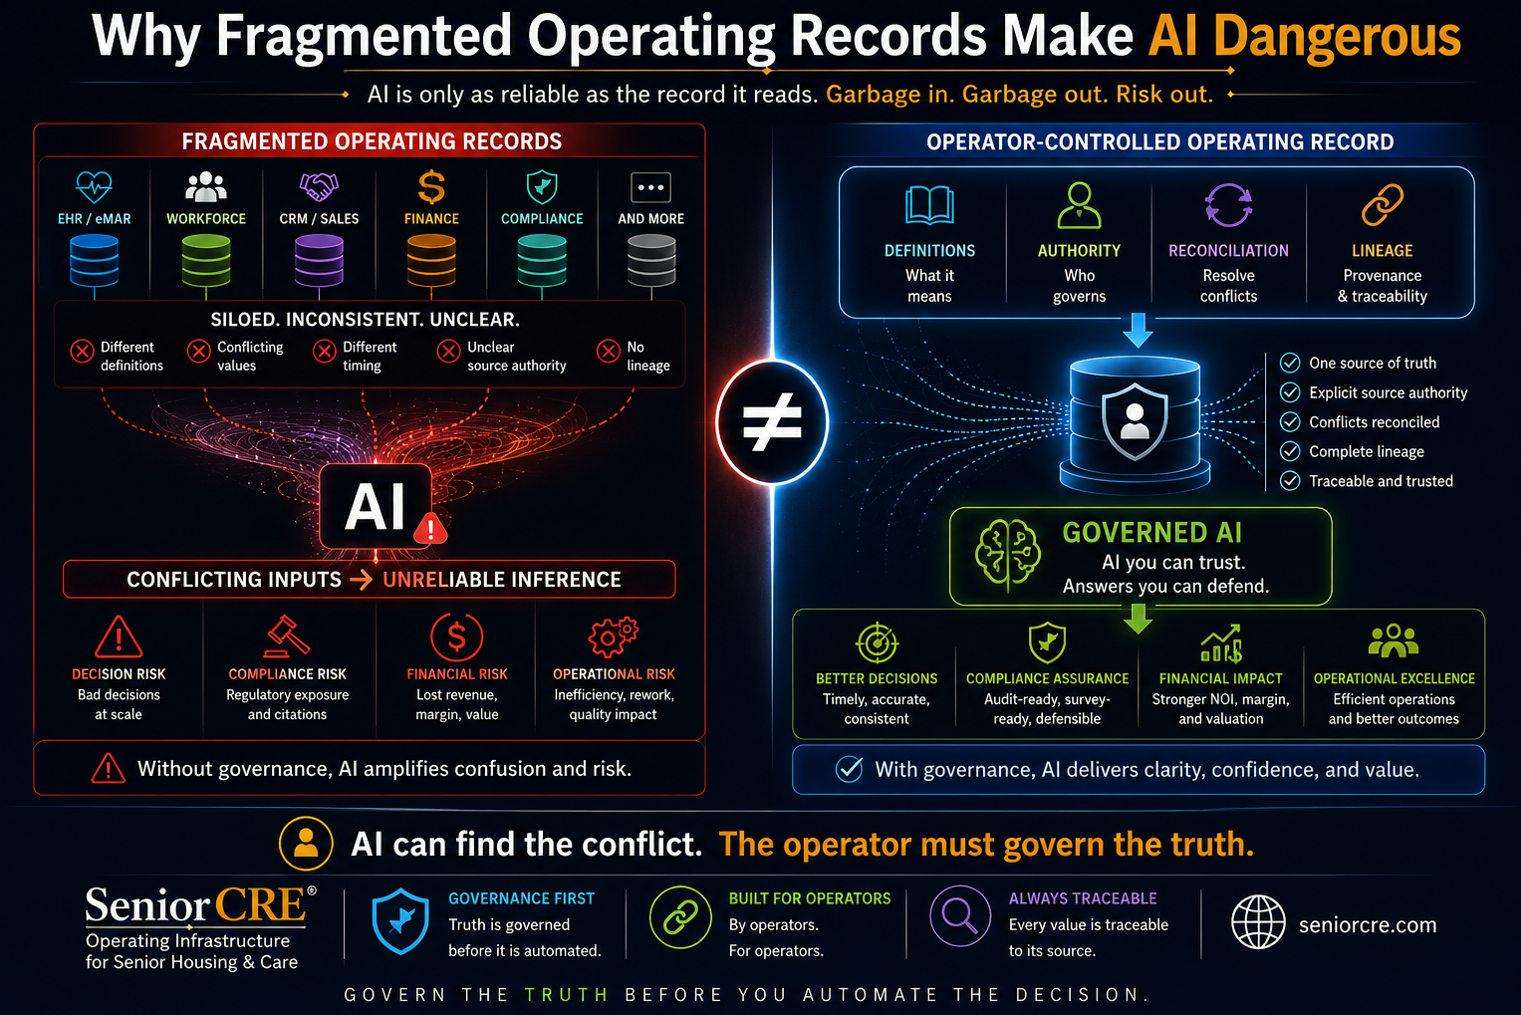
Govern the truth before you automate the decision.
Illustrative governance diagram. It depicts the governance model and design intent, not operator results, customer deployments, production performance, or verified outcomes.
§ The distinction
AI can be intelligent without being authoritative.
A model can find patterns, summarize context, detect anomalies, generate hypotheses and make recommendations. Capability is real. It is also not the same thing as institutional authority.
The organization still has to determine which information governs, which definitions apply, which conflicts require reconciliation, who may accept an inference, and who owns the resulting action.
AI can propose. The operator governs.
§ Where AI sits
AI participates in the operating model. It does not replace it.
DATA
Systems emit what they record, in their own definitions and timestamps.
AI may read
TRUTH
Definitions, source authority, reconciliation and lineage determine what the organization accepts.
Operator-governed
DECISION
A course of action is evaluated against governed facts.
AI may propose
EXECUTION
Authorized action follows, attributable to a named person.
Human authority
Evidence must precede governing truth.Governing truth must precede intelligence.And intelligence must not become execution without appropriate authority.
§ Four different acts
Know, infer, recommend, act. These are not the same activity.
Most conversations collapse all four into “AI making decisions.” Governance depends on keeping them apart.
KNOW
What does the organization actually know, and from which governed source?
The operating record
INFER
What conclusions can be reasonably derived from those governed facts?
AI, inside a defined use class
RECOMMEND
What action is being proposed, with what supporting lineage?
AI, inside a defined use class
ACT
Who holds the authority to cause the organization to act?
A named, authorized human
§ Consequence
Not all AI carries the same consequence.
A summary and an autonomous action are separated by more than capability. They are separated by what happens when they are wrong. That is why classification comes before deployment.
Summarize a variance
Lowest consequence. Nothing changes state.
thenIdentify an exception
A human is directed toward something.
thenInfer a pattern
A conclusion is drawn that was not explicitly recorded.
thenRecommend an intervention
A course of action is proposed.
thenInfluence a material operating decision
Census, staffing, spend, compliance posture.
thenAct autonomously
A fundamentally different authority question — not a fundamentally harder model.
As consequence increases, governance increases. The use classes below are that rule written down.
§ The explainer
The Explainer: AI Governance
Why AI cannot be governed downstream of the data it reads. A walk through definition, authority, reconciliation, and lineage — and what changes when the operator, not a vendor, governs what the business accepts as truth.
Illustrative explainer. Any figures or screens shown are modeled or synthetic and are not operator production results.
§ I · Use classes
Five classes, and one of them is closed
The proposed governance model requires each AI-assisted surface to be classified before reliance. The class determines the review requirement, not the other way around. Class 5 — autonomous action without a human in the loop — is not a roadmap item we have deferred. It is a capability we have declined to build for clinical and regulatory pathways.
Class 1 — Retrieval and summarization over the operator record
Designed — verification pendingProposed scope: read the operator-authorized record and restate it, without adding an assertion or writing back. This record-grounded workflow is not operator validated.
- Examples
- Narrative summary of a variance already computed by deterministic SQL; plain-language restatement of a reconciliation exception.
- Human review
- Not required to read. Required before any summary is exported, attached to a deliverable, or shown outside the operator.
- Data exposure
- Operator-scoped record data inside the tenant boundary.
Class 2 — Classification and routing
Designed — verification pendingAssigns a label, priority, or queue. Changes what a human sees first; does not change the underlying record.
- Examples
- Triaging a reconciliation exception queue; grouping census discrepancies by likely cause; tagging documents by type.
- Human review
- Reviewable and overridable. Design requirement: retain every override, prior label and acting user in the audit history; complete workflow verification remains required.
- Data exposure
- Operator-scoped; classification runs against records already visible to the user.
Class 3 — Operational forecasting and workforce signals
Designed — verification pendingProduces a forward-looking figure or ranking used in a staffing, census, or revenue decision.
- Examples
- Shift coverage risk ranking; census trajectory bands; turnover-risk ordering used to sequence retention conversations.
- Human review
- Required. Output is advisory only, is labeled as a projection, and cannot trigger an action without an accepting user.
- Data exposure
- Operational and workforce data. No published accuracy figure — the platform does not publish model accuracy.
Class 4 — Clinical-adjacent decision support
Designed — verification pendingAnything that could shape a care decision, an assessment, an acuity determination, or a clinical narrative.
- Examples
- Care-plan drafting assistance; acuity change flags; assessment completeness prompts.
- Human review
- Licensed-clinician review required before acceptance. Model output is never the system of record for a clinical determination and is never submitted to a payor or regulator as generated.
- Data exposure
- Highest-consequence class. Proposed boundary: no PHI-bearing third-party model pathway without the required agreement and verified controls; Trust Center governs evidence.
Class 5 — Autonomous action without a human in the loop
Not permittedA model writing to the record, submitting to a payor or regulator, or taking an operational action on its own authority.
- Examples
- Auto-submitting an MDS or PBJ file; auto-adjusting a care plan; auto-posting a billing change.
- Human review
- Not applicable — the class is closed. There is no autonomous-write pathway in the platform and none is planned for clinical or regulatory submissions.
- Data exposure
- None. The capability does not exist.
§ What we declined to build
Some capabilities should not exist.
Autonomous action without a human in the loop is not a deferred roadmap item for clinical and regulatory pathways. It is a capability we have declined to build. No SeniorCRE surface diagnoses, orders, changes medication, or moves a resident on its own authority.
Sophistication is not measured only by how much can be automated. It is also demonstrated by knowing where automation should stop, and saying so before a buyer has to ask.
§ II · Agentic risk
An agent cannot misuse authority it was never given
The emerging enterprise risk is not an inaccurate model. It is an autonomous agent with write authority, acting inside a system of record, at machine speed, without a human who can be held responsible for the result. The durable control is not better monitoring of agent behavior — it is withholding the authority in the first place. When systems disagree, the operator governs; an agent does not.
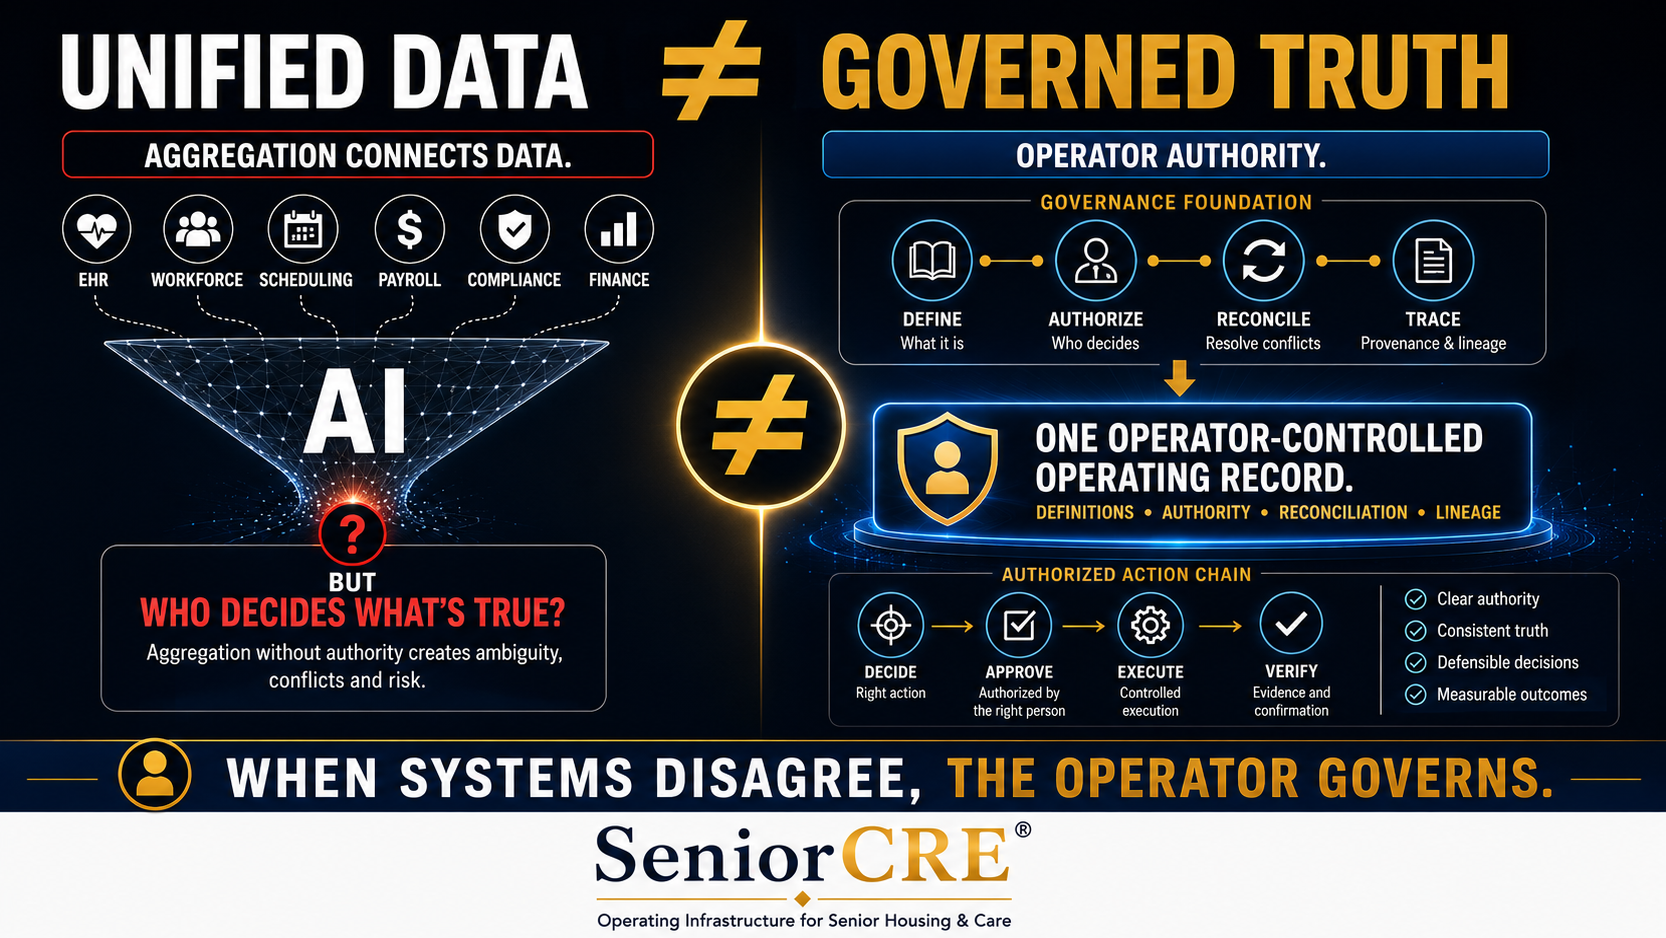
Illustrative governance diagram. It depicts the governance model and design intent, not operator results, customer deployments, production performance, or verified outcomes.
An agent takes an operational action — a submission, a posting, a care-plan change — on its own authority.
Not permittedThe autonomous-action class is closed, not gated. There is no autonomous-write pathway in the platform for clinical or regulatory submissions, so the action is unavailable rather than permitted-with-controls.
Model output silently becomes the number the business acts on.
Designed — verification pendingDesign requirement: keep model output as an attributed suggestion until a named authorized human accepts it. Operating-record admission and its bypass protections require implementation and end-to-end validation.
A prompt is used to widen a query beyond what the requester may see, or to reach across tenants.
Designed — verification pendingRequired boundary: model calls may use only evidence the requesting identity is authorized to read. Verify cross-organization denial and every retrieval path before operator reliance; this page does not establish universal enforcement.
Sensitive data leaves the boundary to reach a model provider, or is absorbed into a vendor training corpus.
Designed — verification pendingPolicy requirement: no PHI-bearing third-party model pathway is offered without the required agreements and validated transmission controls. No operator, resident or workforce training use is authorized by this page. Function-specific data handling evidence must be reviewed through Trust Center.
An AI-assisted entry cannot be reconstructed after the fact, so accountability cannot be established.
Designed — verification pendingDesign requirement: retain prompt inputs and exact prompt/model versions, the accepting or rejecting user and the disposition in immutable history. End-to-end reconstruction evidence for this workflow remains required.
An operator cannot switch an AI surface off for a facility.
In progressPer-tenant disablement is a required control. Complete server-boundary enforcement and bypass testing for this proposed workflow remain verification gates.
Third-party agents or extensions reach the record through a connected tool.
Designed — verification pendingThe proposed starting configuration is read-only. Integrated gateway and MCP policy enforcement remain design intent; each tool path requires scoped authorization, refusal and bypass evidence before reliance.
This register describes design constraints and application controls as of the then-current date. It is not a certification, a threat-intelligence claim, or a statement about any other company's product or incident history.
Direct answer: how to govern AI agents§ III · Context engineering
AI needs governed context, not just more data.
Context engineering is the practice of assembling the information an AI system sees while it performs a task: instructions, retrieved records, policy, workflow history, and available tools. In operations, that is necessary but not sufficient. A model can receive the right documents and still be unsafe if no one has declared which facts govern when systems disagree.
SeniorCRE treats context engineering as a discipline inside AI governance. The Operator-Controlled Operating Record determines what counts as accepted operating truth; the context envelope carries only the slice of that record needed for the task, together with authority, history, and constraints. It is not a fifth stage. EVIDENCE → DISAGREEMENT → AUTHORITY → OPERATOR-CONTROLLED OPERATING RECORD → INTELLIGENCE → EXECUTION remains the operating sequence.
Explore the governed context envelope
The governed context envelope
- Definition
- The metric means the same thing before the model reads it, the executive sees it, and the reviewer reconstructs it.
- Source authority
- The operator declares which source governs for that field, property, period, and decision context.
- Reconciliation
- When valid systems disagree, the model receives the approved rule rather than a larger pile of conflicting facts.
- Lineage
- Design requirement: retain source rows, rule versions, reviewer action and authorization state so an answer can be reconstructed.
- Decision constraints
- The context states what the AI may know, infer, recommend, escalate, and never do without accountable human review.
Explore the context preparation sequence
Operating record
Governed context envelope
AI reasoning
Accountable decision
Authorized execution
Evidence boundary: this section describes the governance architecture and design discipline. It does not assert a completed operator-production deployment, named measured outcome, or independent validation.
§ Velocity
Governance is not the brake. It is what makes intelligence usable.
Without explicit governance
Teams re-debate definitions, re-reconcile spreadsheets, question sources, repeat analysis, escalate disputes, and postpone the decision.
With explicit governance
Definitions already exist, authority is known, exceptions are visible, reconciliation is documented, lineage is retained — and AI can operate inside a known boundary.
§ IV · Data handling and transmission
The questions InfoSec asks, answered before the call
Is PHI transmitted to third-party LLM providers?
Designed — verification pendingNo PHI-bearing third-party model pathway is offered for this proposed operating-record workflow. A policy statement is not a verified transmission control; function-specific PHI boundaries, agreements and testing evidence are governed by Trust Center.
Is operator data used to train models?
Designed — verification pendingThe proposed policy does not authorize operator, resident or workforce data for training or fine-tuning. Verify the provider configuration, agreements and function-specific data flows before introducing private operating data; no cross-operator training permission is implied.
Does one operator ever see another operator’s data through a model?
Designed — verification pendingThe required policy restricts retrieval to the caller’s authorized organization and evidence. Caller-scoped access does not by itself prove every path; cross-organization negative tests and deployed-equivalent verification are required.
Are prompts and outputs retained?
Designed — verification pendingThe proposed record-grounded workflow requires retained prompt/model and policy versions, evidence, reviewer disposition and immutable history. Complete retention and reconstruction evidence remains a gate; transport tracing alone does not establish it.
Can an operator turn AI assistance off?
In progressThe proposed policy requires per-tenant disablement at the server boundary. Verify denial, revocation and direct bypass before reliance; interface controls are not proof of complete enforcement.
Is any clinical data transmitted outbound to a payor, registry, or vendor today?
Designed — verification pendingNo outbound clinical transmission is live in operator production. Submission and exchange surfaces exist as build artifacts built, not yet validated; none is asserted as live at a named operator community.
Is there a customer-managed key or private model deployment option?
PlannedA customer-managed key pathway and a dedicated-inference pathway are on the post-pilot roadmap. Neither is available today and neither should be assumed in a security review.
Operator-data and PHI boundaries require function-specific validation; the Trust Center owns the current evidence posture.
§ V · Framework mapping
Mapped, not certified — and the difference is stated
Most of the frameworks that govern healthcare AI do not issue certificates. NIST AI RMF is voluntary. On ONC health IT certification, the canonical Trust posture governs: SeniorCRE is not certified health IT and is not pursuing ONC / ASTP certification at this time. So each row below says how the framework applies to us and exactly what our posture toward it is — including where the honest answer is “self-assessed.”
NIST AI Risk Management Framework 1.0
NIST AI 100-1 (GOVERN / MAP / MEASURE / MANAGE)Voluntary framework for organizing AI risk practice. Our use-class tiers correspond to MAP (context and consequence), the human-acceptance requirement to MANAGE, and the audit-log reconstruction requirement to MEASURE.
Self-assessed mapping. NIST does not certify conformance and we do not claim any. No third-party assessment against the framework has been performed.
HIPAA Security Rule
45 CFR Part 164 Subpart CAccess control, audit controls, and integrity requirements apply to AI-assisted surfaces exactly as they apply to every other surface. The AI feature inherits the boundary; it does not get an exception.
Trust Center governs the current safeguarding and agreement posture. This is a framework mapping, not evidence that this proposed AI workflow has passed data-handling or operator-readiness gates.
ONC / ASTP HTI-1 decision-support transparency
45 CFR 170.315(b)(11) — Decision Support InterventionsCertified health IT must disclose source attributes for predictive decision support. SeniorCRE is not certified health IT and this criterion does not bind us, so we treat its source-attribute list as the disclosure standard we hold ourselves to for any Class 3 or Class 4 surface.
Voluntary adoption of the disclosure pattern. SeniorCRE makes no ONC certification claim and is not listed as certified health IT.
CMS program integrity expectations
42 CFR Part 483 (SNF requirements of participation)Regulatory submissions — MDS, PBJ, cost reporting — must reflect what a responsible human attests to. This is why the autonomous-submission class is closed rather than gated.
Design constraint, not a compliance claim. SeniorCRE does not certify or attest an operator’s regulatory compliance.
HHS Health Sector AI policy engagement
SeniorCRE white paper response to the HHS Health Sector AI RFIOur published policy position on a tiered governance model for senior care AI, including the argument that governance intensity should track consequence rather than technique.
Published position paper. Not a regulatory approval or endorsement of any kind.
§ VI · What we do not claim
Hold us to this list
- No model accuracy, sensitivity, specificity, or AUC figure is published. Figures of that kind were withdrawn because capability is not outcome.
- No clinical outcome attributable to an AI surface is claimed at any named operator community.
- No third-party AI audit, algorithmic bias audit, or model validation report has been issued, and none is cited.
- No PHI-bearing third-party model pathway is offered for this proposed workflow; agreement and control evidence are governed by Trust Center.
- SeniorCRE is not certified health IT and holds no ONC / ASTP certification.
- NIST AI RMF alignment is self-assessed. NIST confers no certification and none is implied.
- No AI surface is represented as a substitute for licensed clinical judgment, and none is submitted to a payor or regulator without a human attestation.
- End-to-end server-boundary disablement for the proposed operator-governance workflow is not established by this page; permission, refusal and bypass tests remain required.
§ VII · Artifacts available to review
What ships to vendor risk and clinical governance
AI governance white paper (HHS Health Sector AI RFI response)
PublicAI use-class register with per-surface classification
Evidence availability must be confirmed under NDAModel and sub-processor inventory for AI-assisted surfaces
Evidence availability must be confirmed under NDAHuman-acceptance and audit-log control narrative
Evidence availability must be confirmed under NDAAI acceptable-use and clinical-review policy
In draftThird-party AI / bias audit report
Not available — none issued§ VIII · Diligence list
Seven questions to ask every AI vendor, including us
- 01Which of your AI surfaces can write to the record without a human accepting the output?
- 02Does PHI leave your tenant boundary to reach a model provider, and do you hold a BAA with that provider?
- 03Is our data used to train or fine-tune anything you sell to another operator?
- 04Can we reconstruct, months later, which model version produced a given suggestion and who accepted it?
- 05Can we disable an AI surface per facility, and is that disablement enforced at the server or only hidden in the interface?
- 06What accuracy figures do you publish, and what named operator validated them?
- 07Which of your AI outputs have ever been submitted to a payor or regulator without human attestation?
Executive Insights · AI Governance
More capable AI. Clearer decision authority.
A Microsoft-inspired perspective on trusted evidence and human accountability. SeniorCRE’s interpretation—not Microsoft endorsement or validation of our architecture.
Microsoft’s AI Breakthrough: Why Governance MattersTechnical references do not establish production acceptance. Trust Center evidence governs compliance and testing claims.
What makes an operating record governed
“Governed” means more than approved
A record can be complete, auditable, evidence-backed and human-attested and still leave an enterprise question unanswered: which definition had authority to govern this decision?
Senior housing & care enterprises operate across clinical, workforce, occupancy, compliance, financial and capital systems. Those systems can produce different values without any system being wrong. An Operator-Controlled Operating Record preserves those facts, establishes the applicable definition and authority, and records why one meaning governed a particular decision.
A record is not governed merely because:
- The data is centralized.
- Records are unified, matched, merged or deduplicated.
- Institutional context is remembered.
- Evidence is attached.
- A person approved something.
- Every change is logged.
- AI has permissions.
- Workflows follow rules.
- The record is auditable.
Those are important controls, and increasingly standard across enterprise software. Nothing here suggests they are easy or that they are ours. Governed operating truth requires something further.
Seven objects the operator must establish
- 01Definition
What exactly does the fact mean?
The metric, entity, period and measurement moment are written down and approved by the operator — not inherited from whichever system happened to produce the number.
- 02Source authority
Which source is authorized for that definition?
A named system holds authority for that definition, and the reason it holds authority is recorded. Domain systems keep the authority that legitimately belongs to them.
- 03Decision context
For what decision does that authority apply?
Authority is scoped to a decision, not asserted globally. The definition that governs staffing is not necessarily the definition that governs a covenant.
- 04Reconciliation
What happens when another legitimate source differs?
A deterministic rule, written before the disagreement, applied the same way every period, with a stated variance tolerance.
- 05Adjudication
Who possesses authority to resolve disagreement when policy cannot?
A named role, established in advance, whose ruling is recorded against the value — so it does not have to be re-argued next period.
- 06Lineage
Why did this value and this definition govern?
Not only where the number came from. Which definition applied, which source held authority, which rule resolved the difference, and who ruled.
- 07Preservation
What other valid facts existed, and why did they not govern this decision?
Competing legitimate values are kept, not eliminated. A record that deletes the alternative cannot explain the decision it did not make.
Governed truth
Data
Definition
Authority
Decision context
Reconciliation
Governed truth
Decision
Execution
The governing doctrine is unchanged: EVIDENCE → DISAGREEMENT → AUTHORITY → OPERATOR-CONTROLLED OPERATING RECORD → INTELLIGENCE → EXECUTION. These seven objects are what the Operator-Controlled Operating Record contains. Authorization sits between decision and execution; it is not a fifth stage.
Attestation answers: “Who approved this determination?”
Authority answers: “Why did this definition govern this decision?”
Auditability proves what happened. Authority lineage proves why it was allowed to govern.
Definitions, source authority, decision context, reconciliation, adjudication, lineage and preservation are built; external operator deployments have not begun. Enforcement of these objects through a single agent gateway — including any MCP-exposed path — is architecture and design intent on the build roadmap, not a live capability.
Systems hold facts. Decision layers organize evidence. The Operator-Controlled Operating Record establishes what has authority to govern.
AI can reason. The operator governs.
What an AI system should receive before it reasons
Grounding a model in enterprise data is now widely available and increasingly well executed. The narrower requirement is that the model receives the governance state along with the value.
- Governed fact
- The value the operator authorized for this decision.
- Applicable definition
- What that value means, and as of when.
- Authority
- Which source was designated, and on what basis.
- Decision context
- The decision the value was authorized for.
- Conflict state
- Whether a legitimate competing value exists, and whether the difference is resolved.
- Lineage
- Why this definition and value were allowed to govern.
- Permitted use
- What the model or agent may read, act on, or escalate.
If the governance state is unresolved, an AI system should not silently choose which source becomes enterprise truth. It should surface the conflict and escalate to the authority the operator established.
Described here as architecture and design intent. These controls are exercised in SeniorCRE-operated validation environments; enforcement across every AI path in operator production is on the build roadmap and is not presented as a live capability.
Human authority
Human-in-the-loop is necessary, and it is not sufficient
Three concepts are routinely treated as one. They are not the same, and only the third settles an enterprise dispute.
- 01
Human review
A person checks AI output.
- 02
Human attestation
A person takes responsibility for a determination.
- 03
Institutional authority
The organization has established that this person or role possesses authority over this definition or this decision.
SeniorCRE supports review and attestation, and is designed around institutional authority: the record of who was established to decide what governs, before the disagreement occurred.
Who approved it?
Who had authority to decide what governs?
Trusted data is not governed truth
Governing AI is not the same as governing the truth AI acts upon.
Trusted data tells intelligence what it can rely on. Governed truth establishes what the institution has authorized to govern.
AI governance answers
- What may AI access?
- What may it recommend?
- What may it execute?
- When is human approval required?
These are critical, and increasingly standard.
The operator also needs to answer
What is the AI authorized to believe when legitimate systems disagree?
AI governance governs intelligence. The Operator-Controlled Operating Record governs the institutional truth that intelligence depends on.
The executive test
Does your governance control what AI is allowed to do — or also establish what the enterprise is authorized to believe?
If two trusted systems disagree, can you show:
- — the competing values
- — their definitions
- — their sources
- — the authority rule
- — the reconciliation
- — who authorized the determination
- — what decisions relied on it afterward
That is the difference between connected context and governed operating truth.
The more capable AI becomes, the more it matters what it is authorized to believe. The operator decides what governs. SeniorCRE preserves the record of that authority.
Governed truth means the value, definition, or record the operator has authorized for a defined operating purpose — not a claim of universal truth.
Trusted data should be the result of governance — not the assumption that precedes it.
Connected systems provide broader context. Interoperability moves information across workflows. AI can organize that information and support human judgment. Responsible AI governance can constrain how it is used. These are valuable capabilities, increasingly available across enterprise software, and SeniorCRE claims none of them as unique.
Unifying, matching, merging, deduplicating and remembering data can make context cleaner and more useful. None of those operations establishes authority when legitimate systems disagree.
When independently authoritative systems contain different legitimate answers, “trusted data” does not by itself determine which definition applies, which source possesses authority, for which decision, during which effective period, under which exception, or why that meaning governed. An Operator-Controlled Operating Record makes those determinations explicit.
Ground truth is not something a platform gets to declare. The operator declares the definition, assigns source authority, governs reconciliation, and preserves the decision with lineage.
An institutional operator should be able to demonstrate not merely that its data is trusted, connected or interoperable, but why a particular definition and source possessed authority for a consequential decision.
Connected context tells the operator more. Operator authority determines what governs.
Illustrative — not operator data
Which trusted value has authority for this decision?
Operational occupancy
91.7%
Source: trusted · Value: valid
Revenue occupancy
89.9%
Source: trusted · Value: valid
Connected context contains both values. Neither is an error to be eliminated.
- Decision
- Capital planning
- Applicable definition
- Revenue occupancy
- Applicable authority
- Financial Operating Record
- Governed value
- 89.9%
- Alternate valid value
- 91.7% preserved
- Authority lineage
- Recorded
Staffing counterexample
Staffing may legitimately invoke the operational definition instead: operational occupancy governs at 91.7%, while 89.9% remains preserved as a valid revenue value.
Lineage
Why each value governed its decision is preserved — definition, designated source authority, reconciliation state, and the human who adjudicated.
The system should not globally eliminate one value. The operator determines which valid meaning governs each consequential decision.
Trust is important. Authority makes trust institutional.
Definitions, source authority, reconciliation state, lineage and human adjudication are design intent for the Operator-Controlled Operating Record, which is not yet implemented in any community. Enforcement of these controls through a single agent gateway — including any MCP-exposed path — is architecture and design intent on the build roadmap, not a live capability, and none of it runs in external operator deployments today.
Where authority sits
Context explains the enterprise. Authority determines what governs.
Enterprise context describes what the organization knows. Operator authority determines which of several legitimate meanings governs a consequential decision.
Systems of record
EHR, CRM, PMS, workforce, ledger — each independently authoritative for its own domain.
Enterprise context
- Data
- Metadata
- Semantics
- Knowledge
- Policies
- Memory
Increasingly available from major enterprise platforms. A genuine improvement over reasoning across raw, disconnected systems.
Operator authority
- Definition
- Decision context
- Source authority
- Reconciliation
- Human adjudication
- Lineage
Operator-declared, decision by decision. This is the layer SeniorCRE governs.
Governed operating truth
What the organization is authorized to treat as true for this decision.
Approved intelligence
Any authorized model or agent, reading what authority has already established.
Decision
Authorization
Sits between decision and execution. Not a fifth stage of the chain.
Execution
The governing framework is unchanged: EVIDENCE → DISAGREEMENT → AUTHORITY → OPERATOR-CONTROLLED OPERATING RECORD → INTELLIGENCE → EXECUTION. Enterprise context strengthens DATA. Operator authority is what produces TRUTH. When systems disagree, the operator governs.
The model can change. The authority should persist.
AI models, assistants and agents will continue to improve and change, and multiple vendors will supply them. The operator’s institutional definitions, authority rules, reconciliation history, decision rights and lineage should persist independently of the intelligence consuming them.
AI can reason. The operator governs.
The owner sets the standard. The operator retains authority. SeniorCRE makes the authority governable.
- The institutional owner
- Sets the standard it must be able to rely upon — and can require evidence of the control environment without dictating which systems the operator buys.
- The institutional operator
- Retains authority over definitions, source designation, reconciliation and adjudication, and demonstrates how operating truth is governed.
- SeniorCRE
- Makes the operator’s definitions, authority, reconciliation and lineage durable and repeatable across systems and communities.
An owner requires a standard of governance and evidence. It does not select the operator’s software stack.
Controlled execution is not enough
Modern agentic platforms increasingly control AI execution through identity, permissions, deterministic business rules, human approvals, validations, and audit trails. Those controls matter, they are becoming standard properties of enterprise software, and SeniorCRE claims none of them as an invention.
But they begin after another institutional question has been answered: what information is the enterprise authorized to rely upon? If two operating infrastructure contain different legitimate values, an agent can be perfectly authorized to execute while still acting on the wrong definition.
SeniorCRE governs the path from evidence to the Operator-Controlled Operating Record before SeniorCRE Intelligence and controlled execution apply.
Illustrative — not operator data
An AI agent authorized to update the capital forecast
System A
Operational occupancy — 91.7%
System B
Revenue occupancy — 89.9%
Both values are valid.
- Execution question
- May the agent update the forecast? Action policy answers this.
- Upstream question
- Which occupancy definition governs capital planning? Truth policy answers this.
- Decision contextCapital planning
- Applicable definitionRevenue occupancy
- Applicable authorityFinancial operating record
- Governed value89.9%
Only then: AI recommendation → decision → authorization → execution
Permission to execute does not establish authority over truth.
An agent can be authorized to act. The operator still determines what governs.
Definitions, source authority, reconciliation state, lineage and human adjudication are design intent for the Operator-Controlled Operating Record, which is not yet implemented in any community. Enforcement of truth policy and action policy through a single agent gateway — including any MCP-exposed path — is architecture and design intent on the build roadmap, not a live capability.
Where truth is governed
Governed execution requires governed truth.
Execution policy determines what may happen. Truth policy determines what the enterprise is authorized to treat as true before it happens.
Source Systems
EHR, CRM, PMS, workforce, ledger — each preserved exactly as asserted.
Evidence & Provenance
Each assertion bound to its origin, timestamp, definition and lineage.
Disagreement Detection
Material conflicts surfaced, never silently averaged or overwritten.
Operator Authority Chain™
- Definitions
- Source authority
- Reconciliation
- Lineage
- Human adjudication
Operator-declared decision rights: who may decide, for which purpose.
Operator-Controlled Operating Record
The governing determination — what governs for this purpose, and why — with its authority, evidence and lineage.
SeniorCRE Intelligence
Reasons from governed context. Model confidence never creates organizational authority.
Controlled Execution
- Decision rights
- Permissions
- Approval boundaries
- Agent authority
- Audit
Actions only within explicit authority, policy, approval and audit boundaries.
The governing framework is six stages — EVIDENCE → DISAGREEMENT → AUTHORITY → OPERATOR-CONTROLLED OPERATING RECORD → INTELLIGENCE → EXECUTION. Authorization and approval controls occur between decision and execution; they do not become a fifth stage. Govern the truth before you automate the decision. When systems disagree, the operator governs.
§ Doctrine
AI will become more capable.
Models will change. Vendors will change. Agents will become more autonomous.
The institutional questions do not change: Who determines what is true? Who accepts the inference? Who authorizes the decision? Who owns the action? Who remains accountable for the outcome?
Govern the truth before you automate the decision.